When you type an address into your browser, the first letters of the URL determine whether your data travels in the clear or through an encrypted tunnel. HTTPS, which stands for Hypertext Transfer Protocol Secure, adds a layer of encryption to the standard HTTP protocol. This layer relies on the TLS (Transport Layer Security) protocol, the successor to SSL, which protects every exchange between the browser and the web server.
Mixed content and HTTPS migration errors
Installing an SSL/TLS certificate on a site is not enough to fully secure it. A common issue, often overlooked, occurs after migration: mixed content breaks HTTPS protection.
Have you ever noticed a crossed-out padlock or a browser warning on a site that is supposed to be HTTPS? This happens when certain resources (images, scripts, stylesheets) are still loaded over HTTP. The browser then considers the page to be partially insecure.
Fixing this issue requires rewriting all internal URLs to point to HTTPS resources. Cloudflare offers automatic rewrites to handle this specific case. On a CMS like WordPress, plugins like Really Simple SSL make this correction easier. For those who want to learn everything about the acronym HTTPS and how it works, managing mixed content is a necessary step before considering the migration complete.
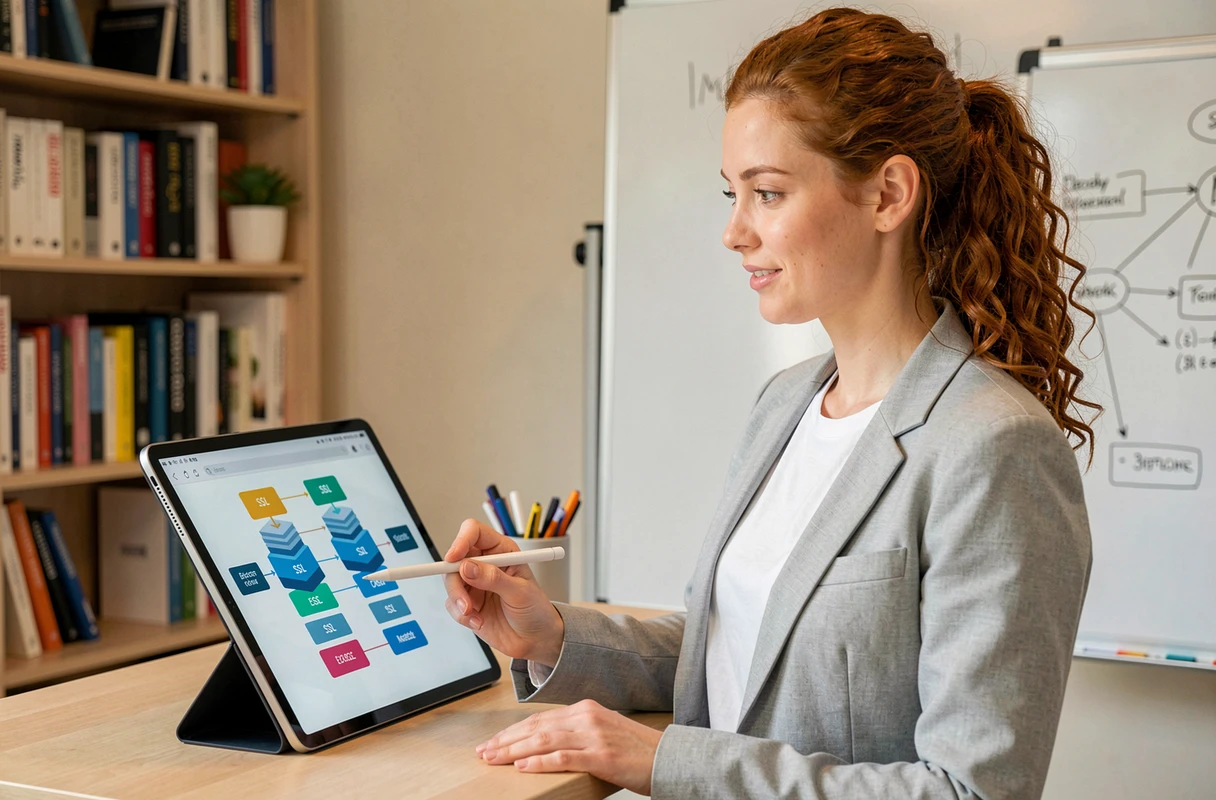
SSL/TLS certificate and encryption: how the connection is secured
The security mechanism relies on two distinct steps. The first uses asymmetric encryption to exchange keys. The second switches to symmetric encryption, which is faster, to protect data throughout the session.
The role of the certificate and the certification authority
A digital certificate is issued by a certification authority (CA). This certificate proves to the browser that the server is indeed what it claims to be. Without this verification, an attacker could impersonate the legitimate site.
The certificate contains the server’s public key. The browser uses it to encrypt a shared secret, which only the server can decrypt with its private key. This secret is then used to generate session keys for symmetric encryption.
TLS 1.3 and its concrete improvements
TLS 1.3 reduces the number of exchanges needed to establish a secure connection. The result: faster negotiation and the elimination of outdated algorithms that were still tolerated by previous versions. Current work focuses on post-quantum cryptography, designed to withstand future quantum computers capable of breaking classical encryption algorithms.
HSTS: forcing the browser to stay on HTTPS
Configuring HTTPS on your domain does not guarantee that every visitor will use it. A user who manually types an address without the “https://” prefix can be redirected to HTTP for a fraction of a second. This window is enough for a downgrade attack.
HSTS (HTTP Strict Transport Security) instructs the browser to accept only encrypted connections for a given domain, for a duration defined by the server. Specifically, the server sends a specific header in its HTTP response. The browser remembers it and then refuses any unencrypted connection, even if the user types “http://”.
This mechanism is distinct from a simple 301 redirect from HTTP to HTTPS. The redirect fixes the problem on the server side. HSTS fixes it on the browser side, even before an HTTP request is sent. Recent hardening guides recommend HSTS as a full-fledged security control.
HTTPS does not protect everything: complementary measures
A site on HTTPS encrypts data in transit between the visitor and the server. But threats are not limited to network interception. HTTPS does not protect the server itself or the web application.
Here are the measures that truly complement the encryption of the connection:
- The Secure, HttpOnly, and SameSite cookie attributes limit the exposure of session tokens. Secure prevents the cookie from being sent over an HTTP connection. HttpOnly blocks access to the cookie by client-side JavaScript. SameSite reduces the risk of CSRF attacks by controlling when the cookie is transmitted.
- Regular updates of the CMS and its plugins fix known security vulnerabilities. An outdated WordPress or PrestaShop remains vulnerable, certificate or not.
- Two-factor authentication (2FA) on admin accounts adds an extra barrier against unauthorized access, even if a password leaks.
- Tested backups allow for site restoration after an incident. An unverified backup is almost as risky as having no backup at all.
Check the HTTPS security of your website
Several indicators allow you to quickly check if your domain is properly configured. The padlock icon in the address bar remains the most visible signal for visitors. By clicking on it, the browser displays the certificate details: issuing authority, expiration date, covered domain.
Online SSL verification tools analyze the server configuration more deeply. They detect outdated TLS versions still active, weak cipher suites, or the absence of an HSTS header. A valid certificate does not mean that the TLS configuration is optimal.
Also, remember to monitor the expiration date of your certificate. An expired certificate triggers a full-screen warning in the browser, which drives away visitors and can affect your ranking in search engines.
The security of a website works in successive layers. HTTPS is the first, which protects the communication channel. Secure cookies, HSTS, updates, and 2FA form the subsequent layers. Neglecting any of them weakens the whole, regardless of the care given to the others.